 7 min read
Does Copilot respect SharePoint permissions?
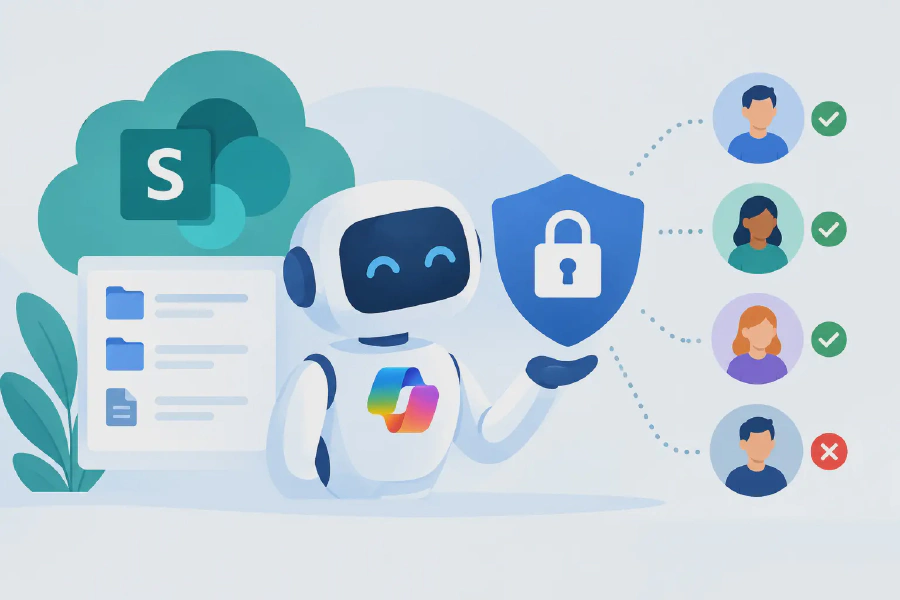
Copilot can turn a question such as “What did we agree in last quarter’s supplier review?” into a useful answer in seconds. That capability naturally raises a more serious question for IT and business leaders: does Copilot respect SharePoint permissions? The short answer is yes. Microsoft 365 Copilot is designed to honour the permissions already applied to SharePoint, OneDrive and other Microsoft 365 services. The practical answer, however, is that Copilot may make existing access far more visible than it has ever been before.
For organisations preparing for Copilot, this is not primarily an AI problem. It is an information governance problem. If users can already access poorly managed, outdated or overly broad SharePoint content, Copilot can help them find it, interpret it and reuse it faster.
How Copilot respects SharePoint permissions
Microsoft 365 Copilot works within the signed-in user’s identity and access rights. When it retrieves information through Microsoft Graph, it is intended to retrieve only content that the user is already authorised to access. Copilot does not grant a staff member permission to a restricted site, library, folder, file or page simply because they ask a well-worded question.
For example, a finance manager with access to a confidential board library may receive Copilot responses grounded in documents from that library. A staff member without access to the library should not receive those documents, their contents or a summary based on them. The same principle applies where SharePoint permissions are inherited from a site, managed through Microsoft 365 groups, or broken at library, folder or individual-file level.
This is the core assurance: Copilot is permission-aware, not permission-bypassing. It respects the access model you have configured.
Copilot can reveal what was already available
The distinction matters. Before Copilot, a document may have been technically accessible but difficult to locate. It might sit in a large team site, carry an unclear file name, or be buried several folders deep. A user might never have found it through conventional search.
Copilot changes the experience. It can bring together content from files, meetings, emails and SharePoint pages in response to a natural-language prompt. That can expose the consequences of broad access arrangements that have gone unnoticed for years.
A common example is an “Everyone except external users” permission on a site containing draft policies, commercially sensitive documents or HR material. Copilot has not created the exposure. It has made the exposure easier to recognise. That is why an AI readiness assessment should examine not only technical controls, but also who can access information and whether that access remains appropriate.
Where SharePoint permission risk still exists
SharePoint permissions are effective only when they are deliberately designed and maintained. Copilot respects SharePoint permissions, but it cannot determine whether a permission model reflects your organisation’s current structure, responsibilities or risk profile.
Broad memberships are often the largest issue. Users may retain access after moving roles, completing a project or leaving a department. Teams may use large Microsoft 365 groups for convenience, then store sensitive information in connected SharePoint sites. Site owners may share individual documents directly without reviewing access later. Over time, these decisions create a permission landscape that is difficult to explain and even harder to govern.
Item-level permissions can also introduce complexity. Restricting a small number of files or folders may seem sensible, but extensive unique permissions make sites harder to administer, audit and support. In many cases, separating confidential content into a dedicated site or library with a clear membership model is easier to manage and more reliable at scale.
There is also a content-quality consideration. Copilot may draw from documents a user can access even when those documents are old, duplicated or no longer approved. The risk is not necessarily unauthorised access. It may be that a user receives an answer based on an obsolete procedure when the current version exists elsewhere.
What Copilot does not fix for you
Copilot is not a replacement for SharePoint governance, records management or document lifecycle controls. It will not tidy disconnected sites, remove stale permissions, identify the authoritative version of every procedure or decide which documents should be retained.
Sensitivity labels, retention labels and data loss prevention controls remain valuable parts of a wider information protection strategy. But they must be configured for the outcome you need. A label that signals confidentiality is useful for classification and user awareness; a label with encryption and access restrictions can provide stronger protection. Retention controls help manage lifecycle requirements, but they do not automatically correct excessive SharePoint membership.
Likewise, a polished intranet does not guarantee safe Copilot use if document libraries behind it are unmanaged. Organisations need both: an easy-to-use experience for staff and an information architecture that supports clear ownership, access and lifecycle decisions.
Preparing SharePoint for Copilot with confidence
The most effective preparation starts with the content that matters most, rather than attempting to review every file in the tenant at once. Focus first on sites holding personal information, commercial documents, executive material, legal content, clinical or student records, controlled policies, and operational procedures that staff rely on daily.
A practical review should establish who owns each site and library, who has access, why they have access, and whether the content is current. Where a site has no active business owner, that is a governance issue worth resolving before Copilot adoption expands.
Then consider the information experience. Approved policies should be clearly identified and easy to find. Drafts and working files should not sit beside published material without clear status. Archived content should be managed so it does not compete with current guidance. Naming conventions, metadata and document review processes are not administrative extras - they directly improve the reliability of Copilot responses.
For high-risk content, use a deliberate site and membership design. A dedicated restricted site is often preferable to relying on numerous exceptions inside a broadly accessible workspace. Keep owners accountable, use groups rather than assigning access person by person where possible, and establish a process for regular access reviews.
Use real prompts to test real exposure
Permission reviews should not remain theoretical. Test the experience from the perspective of different user roles. Ask representative questions that staff are likely to ask, such as requests for current policies, project decisions, customer information or departmental plans.
This testing can reveal several useful findings. You may identify a staff member with access they no longer need, a site that contains duplicated procedures, or a business area where information is stored in too many locations. It can also build confidence by demonstrating that restricted material is not returned to unauthorised users.
Testing should include the tools employees will actually use. Copilot in Teams, Word, Outlook and the Microsoft 365 experience may surface information in different working contexts, even though the underlying permission principle remains the same. The goal is to validate the day-to-day experience, not just the configuration screen.
Governance should support adoption, not slow it down
The strongest Copilot programmes balance control with usability. Blocking AI access to everything may reduce immediate concern, but it also prevents teams from gaining value from the knowledge they are entitled to use. Allowing unrestricted adoption without reviewing SharePoint can create avoidable risk and undermine staff trust.
A staged approach is usually more effective. Start with a defined group, prioritise well-managed sites and high-value use cases, and use what you learn to improve content and controls. Establish clear responsibilities between IT, information management, security, business owners and communications teams. Each group sees a different part of the problem, and all are needed for a sustainable result.
For organisations with critical policies and mandatory reading requirements, governance should also include evidence of engagement. A document being accessible is not the same as it being read and acknowledged. Solutions such as Compliance Tracker 365 can help organisations identify the right audience, distribute critical content and maintain visibility of acknowledgements alongside broader SharePoint governance.
Copilot can be a powerful prompt to address long-standing information management issues. Treat that prompt as an opportunity: organise content around business purpose, give owners clear responsibility, and make trustworthy information easier for the right people to use.