 7 min read
Microsoft 365 information architecture guide
When staff cannot tell whether a file belongs in Teams, SharePoint, OneDrive or an email attachment, the issue is rarely user behaviour alone. It is usually a design problem. This Microsoft 365 information architecture guide explains how to create a structure that makes information easier to find, govern and use - without turning your digital workplace into a maze of sites, folders and duplicate documents.
Information architecture is the practical blueprint for how content is organised, labelled, stored and surfaced across Microsoft 365. Done well, it supports daily work while giving IT and business leaders the control needed for retention, security, compliance and AI readiness.
Why Microsoft 365 information architecture matters
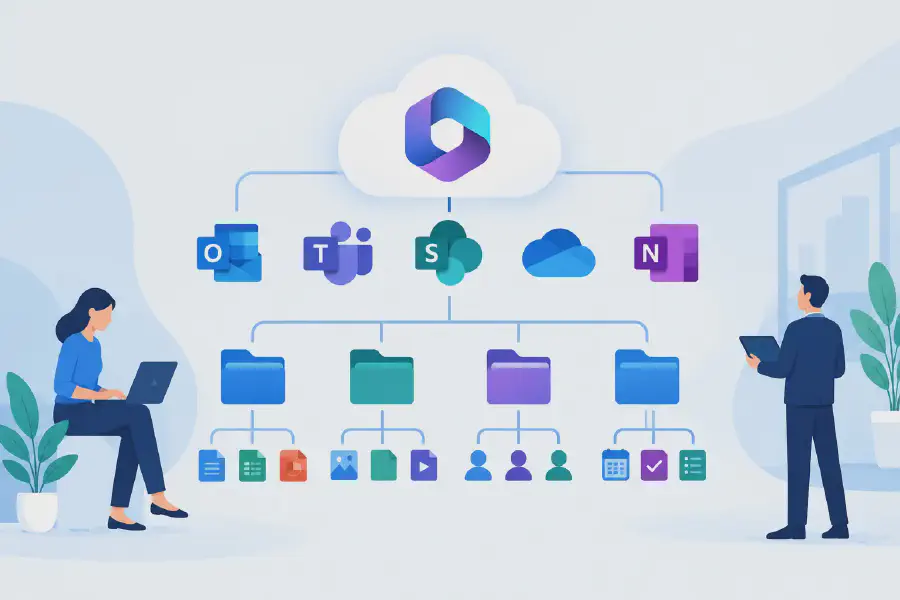
Microsoft 365 gives organisations several powerful places to work. Teams supports collaboration, SharePoint supports structured content and communication, OneDrive supports individual work in progress, and Outlook remains central to formal communication. The challenge is not a lack of options. It is deciding where each type of information should live and how people should find it later.
Without clear architecture, familiar problems appear quickly: multiple versions of the same policy, project teams creating sites with inconsistent permissions, folders growing ten levels deep, and staff searching by guesswork. These issues slow work down, increase compliance risk and reduce trust in the platform.
The stakes are higher for organisations preparing to use Microsoft Copilot. AI can only provide useful, appropriate responses when content is well structured and permissions are accurate. Copilot does not repair poor governance. It can expose it faster.
Start with business tasks, not Microsoft 365 features
A common mistake is to begin with a technical decision: “We need a new SharePoint site” or “Every department needs a Team.” A better starting point is the work people need to complete.
Map the key information journeys across the organisation. For example, an employee may need to locate a current HR policy, submit a procurement request, collaborate on a project brief, or confirm they have read an updated clinical procedure. Each journey has different requirements for ownership, access, approval, retention and acknowledgement.
Ask practical questions before designing the structure. Who creates the information? Who needs to read, edit or approve it? Is it temporary collaboration material or an official organisational record? How long must it be retained? Does a staff member need to acknowledge it?
This approach prevents a technically tidy environment that does not match how the business actually operates. It also helps distinguish between content that should be shared broadly and content that requires restricted access.
Define clear homes for content
A useful architecture gives people simple rules they can apply without consulting a manual. The precise model depends on the organisation, but the following distinctions are usually effective.
OneDrive is for individual working files and drafts that have not yet become team or organisational content. It is not a long-term repository for records that others need to access.
Teams is for active collaboration within a defined group, project or operational team. Files shared in Teams are stored in SharePoint, so Teams should be designed with its connected SharePoint site in mind rather than treated as a separate file system.
SharePoint team sites suit structured departmental and project content, particularly where libraries, metadata, controlled permissions and business processes are needed. They are often the right home for business records and repeatable operational material.
SharePoint communication sites or intranets suit published information intended for a wider audience, such as policies, news, procedures, service information and organisational resources. These sites need clear publishing ownership so employees can trust that what they read is current.
The aim is not to eliminate every exception. It is to ensure exceptions are deliberate, documented and manageable.
Build a navigation and taxonomy model people understand
Navigation should reflect the language of the organisation, not the internal structure of Microsoft 365. Employees search for “leave”, “supplier onboarding” or “incident reporting”; they do not search for an information architecture diagram.
Start with a small, agreed taxonomy: the common terms used to classify content. This may include department, business function, document type, client, project, status, confidentiality level or financial year. Use terms that are meaningful, stable and useful for finding or governing content.
Metadata is valuable when it solves a real retrieval or compliance problem. For a policy library, fields such as policy owner, review date, policy category and approval status can make content easier to filter and maintain. For project documents, project name, workstream and document status may be more useful.
Do not apply metadata to every file simply because the platform allows it. Overly complex forms encourage staff to select the first available option or avoid using the library altogether. The best model balances consistency with effort.
Folders still have a role, especially where teams need a familiar way to browse active work. However, folders should not be the only organising method. A combination of shallow folders, useful metadata and views is usually more scalable than an ever-expanding folder tree.
Design governance into the structure
Governance is not a policy document that sits unread in a separate folder. It should be visible in the way sites are requested, created, owned and reviewed.
Every site and Team should have accountable business owners. Those owners need to understand what they are responsible for: managing membership, maintaining content, reviewing access and deciding when the workspace is no longer required. IT can provide guardrails, but it cannot own the meaning and quality of every department’s content.
A practical governance model sets standards for naming, site templates, external sharing, sensitivity labels, retention and lifecycle management. It should also include a straightforward request process for new workspaces. If the approved process is too slow or difficult, staff will create unmanaged alternatives.
Permissions deserve particular care. Broad access can make knowledge sharing easier, but excessive access may expose confidential information or produce poor Copilot outcomes. Conversely, highly fragmented permissions create administrative burden and make collaboration difficult. Group-based access, with a small number of well-defined roles, is generally easier to manage than file-by-file permissions.
Treat published content as a controlled service
Policies, procedures and critical organisational pages require more than an attractive intranet layout. They need an operating model.
Define who drafts, approves and publishes each content type. Set review dates and assign owners. Establish what happens when a policy is superseded, and ensure the current version is easy to locate while old versions are retained or disposed of according to requirements.
For high-risk content, visibility alone may not be enough. Organisations in healthcare, education, government and regulated services may need evidence that specific staff have seen and acknowledged a document or page. Compliance Tracker 365 can support this requirement by assigning critical content to the right people and reporting on acknowledgement status. This turns an intranet page or document library into a more accountable compliance process.
Plan for search and Copilot from the beginning
Search is often the real test of an information architecture. A user should be able to locate a current document through sensible titles, metadata, filters and managed navigation without needing to know the site where it was stored.
Create naming conventions that distinguish content clearly. “Procedure - Incident Management - Approved” is more useful than “Final v7”. Encourage meaningful document titles and avoid relying on filenames alone to explain status or ownership.
For Copilot readiness, focus on three areas: content quality, permissions and information lifecycle. Remove or archive obsolete material where appropriate, make authoritative content identifiable, and check that access reflects genuine business need. The goal is not to make every document available to everyone. It is to make trusted information available to the right people.
Implement in stages and measure adoption
Large-scale restructures can create unnecessary disruption. A staged approach usually delivers better results: begin with a high-value business area, validate the model with real users, then apply lessons before expanding.
Measure more than migration volume. Look at whether users can find key content, whether duplicate documents are decreasing, how many unmanaged sites exist, whether owners complete reviews, and whether critical content acknowledgements are being recorded. Short feedback sessions with staff often reveal issues that analytics alone will miss.
Training should be role-based. Site owners need guidance on governance and permissions, while general users need simple direction on where to save, find and share information. Clear rules, reinforced in the flow of work, are more effective than lengthy platform training.
A well-designed Microsoft 365 environment does not ask employees to memorise a complex framework. It gives them sensible places to work, trusted information when they need it, and clear accountability when that information matters most.